www.it-connect.fr
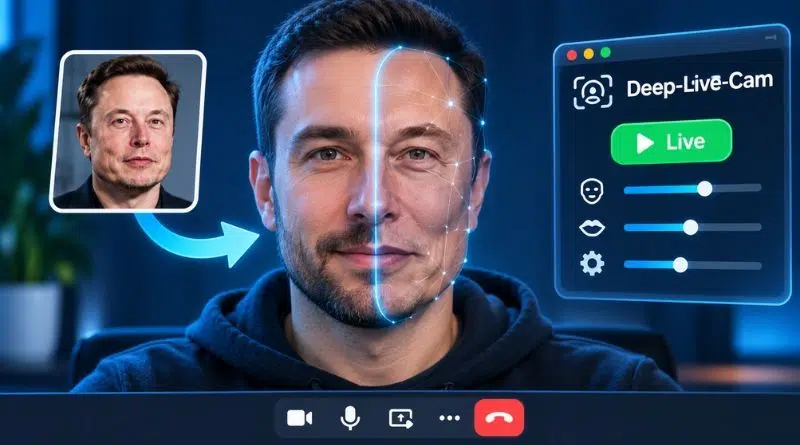
Deep-Live-Cam: The Open-Source Deepfake Tool That Replaces Your Face from a Photo
Discover how Deep-Live-Cam creates real-time deepfakes from a single photo, and learn why IT teams should prepare now.
Read the post
Discover how Deep-Live-Cam creates real-time deepfakes from a single photo, and learn why IT teams should prepare now.
Read the postLearn how to install Cloudflare’s security-audit skill and run AI-assisted security audits with Claude Code, results, and limits.
Read the postDiscover the four identity security gaps attackers target and learn how to secure creation, login, session, and recovery with Specops.
Read the postDiscover how REA lets Claude Code drive Ghidra to analyze binaries, recover game rules, and recreate software from scratch.
Read the postLearn how DNS exfiltration works, spot its warning signs in logs, and deploy practical controls to block silent data leaks.
Read the postLearn what WPAD does on Windows, the security risks it creates, and how to disable it cleanly with GPO and Registry settings.
Read the postLearn how deepfakes, voice cloning, and vishing bypass identity checks—and discover the best ways to secure access and verify users.
Read the postDiscover how a malicious UpdraftCentral plugin was installed via UpdraftPlus, why the attack failed, and how to check your WordPress site.
Read the postDiscover how to analyze Chrome and Edge artifacts in Windows forensics: history, downloads, cookies, logins, bookmarks, and more.
Read the postLearn how to trace USB devices in Windows using Registry keys, logs, and NirSoft tools to identify devices, users, and dates.
Read the postExplore how public detection rules help defenders, how attackers bypass them, and why behavioral detection must complement signatures.
Read the postLearn how device trust secures BYOD and contractor access without MDM, using continuous posture checks and Zero Trust controls.
Read the postLearn how to find, access, and extract data from Windows Shadow Copies with vssadmin, mklink, and ShadowCopyView.
Read the postLearn how to analyze Windows Jump Lists with JLECmd, extract usage traces, and correlate artifacts for stronger forensic timelines.
Read the postDiscover where MFA fails in hybrid environments and how to close Active Directory blind spots with Specops Secure Access.
Read the post