www.it-connect.fr

PHP2Shell and Fragnesia: The Attack Chain That Gained Root on 24 Firewalls
By chaining the exploitation of the PHP2Shell vulnerabilities and the Fragnesia flaw in the Linux kernel to compromise firewalls, cybercriminals managed to pull off a highly effective attack. Out of 240 firewalls targeted, 24 were compromised and the attackers managed to obtain root privileges. Here is what we know about these cyberattacks.
Things are still moving on the known security flaws front (including some already patched). The US CISA has just added the CVE-2026-46300 vulnerability, aka Fragnesia, to its KEV (Known Exploited Vulnerabilities) catalog. This has consequences in the US: federal agencies must now patch it if they have not already done so, and the deadline is very short, as it is set for Saturday.
Fragnesia: the name may sound familiar. It is a vulnerability discovered last May in the Linux kernel that provides local root access. It belongs to the Dirty Frag family of flaws and affects Linux kernels released before May 13, 2026. What you need to understand is that Fragnesia alone requires local access to the machine.
This is where PHP2Shell comes into play. These two critical flaws (CVE-2026-109618 and CVE-2026-109619) allow unauthenticated remote code execution and were patched on October 21 in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. CISA itself added them to the KEV catalog on Monday, October 26.
"This vulnerability can be chained with CVE-2026-109618 and CVE-2026-109619 to deploy PHP web shells and execute commands as root.", the US agency notes about Fragnesia. This means that PHP2Shell and Fragnesia can be exploited together. PHP2Shell opens the server door, while Fragnesia provides the keys by granting access to the root account.
25 Devices Compromised by These Flaws
CISA considers these vulnerabilities exploited, and especially exploitable together, without detailing these attacks. It is a Dream Security report that provides answers about the cyberattacks observed. Indeed, Dream Security researchers recovered the artifacts from a complete operation: a custom PHP2Shell exploit paired with Fragnesia, target lists, logs, and around forty post-exploitation scripts.
The famous targets are not classic web servers running PHP, but firewalls from a major vendor whose name has not been disclosed (this vendor was notified). The administration interface relies on a less maintained version of PHP, namely PHP 8.0.30 (however, patches have been released).
Here is the scenario of this attack campaign:
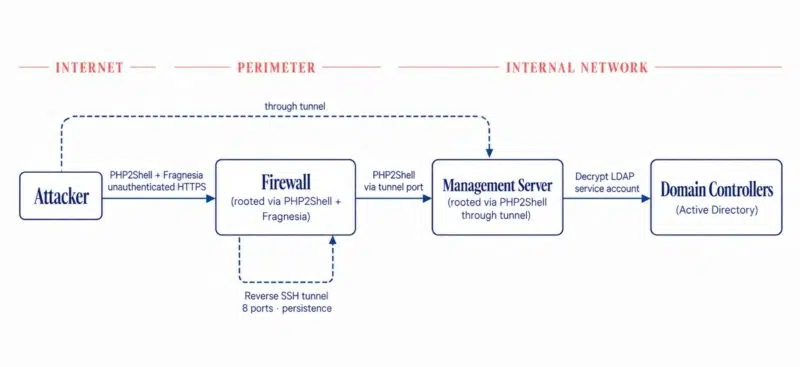
- Reconnaissance and filtering: about 19,000 exposed firewalls were identified via FOFA, a Chinese search engine comparable to Shodan. After filtering the potential targets (notably by version), only 240 firewalls were actually targeted, in the United States, Japan, Taiwan, and South Korea.
- Exploitation: PHP2Shell provides code execution under the nobody account, then Fragnesia overwrites the
/etc/pam.d/sufile in the page cache so thatsu rootworks without a password. All of this in less than 15 minutes. Result: 24 firewalls compromised, each infected with a PHP web shell. - Pivot: two of these firewalls belonged to an organization affiliated with the US government. Through a reverse SSH tunnel, the attacker compromised the firewall management server (counted as the 25th device), then went after Active Directory.
"An AD attack campaign was launched from the management server. Since the management server already had an LDAP connection to Active Directory (required to authenticate VPN users), the attacker used it as a launch platform to conduct attacks against the domain.", we can read.
Dream does not attribute the operation to a specific hacking group, but several clues point to an actor linked to China (starting with the use of FOFA and the use of the DeepSeek and Kimi models).
These are further reasons to protect yourself against the PHP2Shell and Fragnesia flaws. It would also be useful to know more about these famous firewalls... One technical detail, however, suggests Palo Alto Networks: the exploit targets the firewall management server called "appweb". It is precisely under /var/appweb that the PHP scripts for the PAN-OS administration interface are located. The compromised management server would then point to Panorama. This is only a hypothesis, which neither Dream nor Palo Alto has confirmed. It is consistent with Palo Alto's security bulletin, updated on October 29: PAN-OS and Panorama are listed among the products affected by PHP2Shell. “Active exploitation has been observed, targeting the Palo Alto Networks administration interface exposed on the Internet.”, the vendor notes. More to come...