www.it-connect.fr

Microsoft’s Official X Account Hacked to Promote a Clippy-Themed Crypto Token
Microsoft's official X account, followed by 13 million users, was hijacked by hackers who used Clippy as bait. Microsoft has confirmed that unauthorized access did occur. Here's what we know.
On Thursday, October 1, 2026, hackers took control of Microsoft's official X account, @Microsoft. They used it to promote @clippymsftcto, an account impersonating Clippy, the famous Office assistant, with no connection to Microsoft. The compromised account began following it, then reshared one of its posts in an attempt to lure X users into a trap...
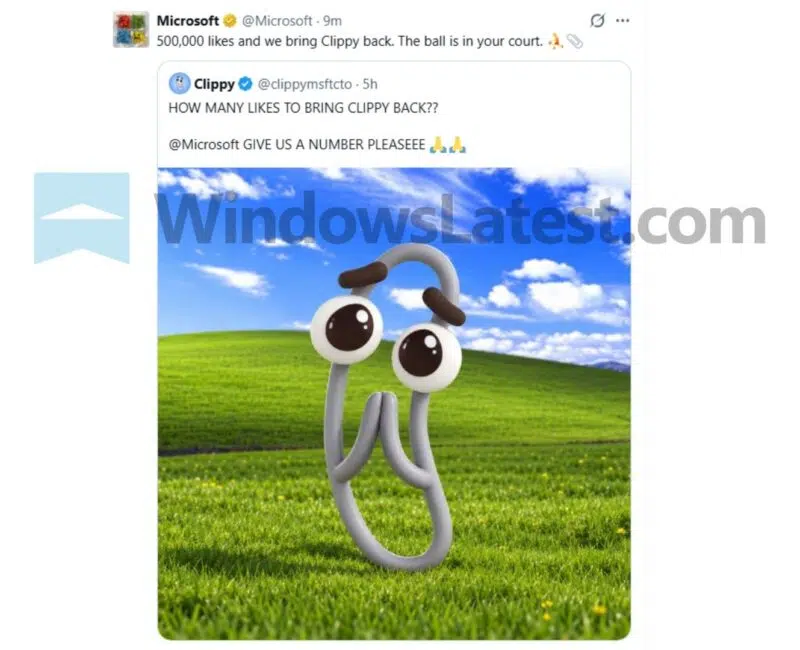
The account in question had posted an image of Clippy in front of the iconic Windows XP wallpaper, asking: "HOW MANY LIKES TO BRING CLIPPY BACK ??". "500,000 likes and we bring Clippy back. The ball is in your court", replied the hijacked Microsoft account in a quote post, according to Windows Latest. The whole thing was orchestrated by the hackers who had taken over Microsoft's X account.
Enough to delight nostalgic Windows and Office users, but in this case, there was no Clippy magic—just cryptocurrency. The goal was financial: to leverage the credibility of Microsoft's account to draw buyers toward a cryptocurrency token.
The @clippymsftcto account has since been suspended, but another account, @ClippyMSFT, continues to promote a token called $Clippy. It claims that it has "a liquidity pool directly associated with $MSFT", Microsoft's stock ticker. The scheme looks very much like a classic pump-and-dump: artificially inflating a token's price by using the reach of a high-profile account, then selling at the top at the expense of late buyers.
A fake excuse, also posted by the hackers
A little later, another post appeared on Microsoft's account, all the while looking like an official denial. "We are aware of a cryptocurrency token being promoted in connection with the $MSFT stock, including the unauthorized use of the Clippy brand and Microsoft intellectual property. Microsoft did not authorize, sponsor, endorse, or permit the creation, promotion, or use of any cryptocurrency token associated with Clippy, Microsoft, or $MSFT", the post read. According to Windows Latest, the message also mentioned legal action.
Except that this message did not come from Microsoft either. A spokesperson confirmed to Windows Latest that the account posted two unauthorized messages during the breach: the quote from the fake Clippy account and this fake apology. A denial written by the hackers themselves... enough to muddy the waters. I still wonder what the point of that message was? Maybe to make it look like Microsoft had regained control, or to buy time, or simply to generate even more attention for the token, since it still links Clippy to the $MSFT stock...
Once Microsoft was able to regain control of its X account, the incident was confirmed. "We confirmed unauthorized access to our X account, including posts that did not come from Microsoft. The account has been secured, the unauthorized posts have been removed, and we continue to investigate the circumstances". One question remains: how did the hackers take over Microsoft's X account? Don't tell me there was no MFA...
This incident is a useful reminder about securing business accounts on social networks. They are assets that must be configured:
- Strong authentication: prefer security keys or passkeys over SMS codes.
- Restricted access: limit the number of people authorized to post.
- Third-party applications: review scheduling and management tools authorized to post on behalf of the account.