www.it-connect.fr
Veeam Agent for Windows CVE-2026-32996 Gives SYSTEM Privileges, Public Exploit Released
If you use Veeam Agent for Windows version 13 and haven’t updated it in a while, it’s time to act. A security flaw patched last May is back in the spotlight: a public exploit has been available since September 14, 2026. Here’s what you need to know.
This vulnerability, tracked as CVE-2026-32996, is not new. A quick look at Veeam’s website shows that it was patched on May 27, 2026, with the release of Veeam Backup & Replication 13.0.2.29. But with summer in full swing, you may have missed it. In its security bulletin, Veeam explains that this flaw in Veeam Agent for Windows allows local privilege escalation (CVSS v4 score of 7.3 out of 10).
However, in recent days (September 14, 2026), the situation has changed for this vulnerability. Indeed, a detailed technical analysis was published on a blog and is accompanied by exploit code on GitHub. The question now is: is this vulnerability being exploited by cybercriminals?
And here, I have my doubts. Let me explain. Following the publication of the exploit code, Arctic Wolf published a bulletin dedicated to CVE-2026-32996 to note "UPDATE: Active Exploitation CVE-2026-32996 of Veeam Agent". The flaw would therefore be used in attacks, except that this article was removed a few days later. Naturally, that makes me doubt it.
For its part, Veeam does not report any exploitation in its security bulletin, and I have found no other source confirming attacks. Caution is advised.
A session identifier left behind in a log file
Even if there is some confusion around the exploitation of this vulnerability, that doesn’t stop us from discussing it and protecting ourselves against it. The exploit code is indeed available... In the case of CVE-2026-32996, the issue lies in the VeeamEndpointBackupSvc service, which drives the Veeam agent on Windows.
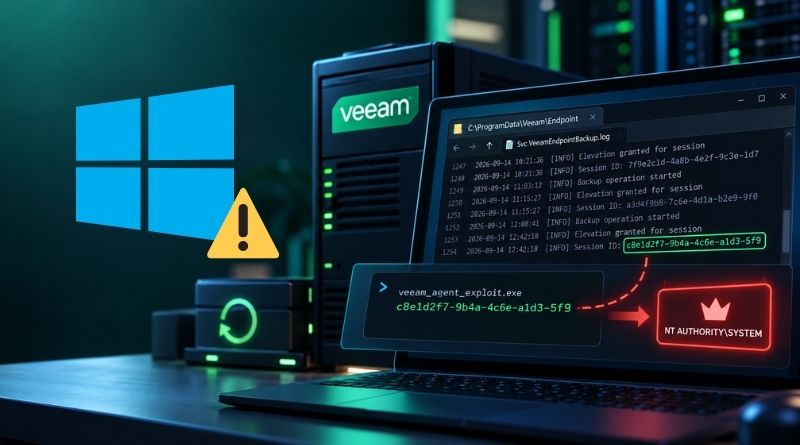
When an administrator opens the agent with elevated privileges, the service assigns a session identifier, a kind of access ticket. The problem is that this ticket is not tied to its owner: anyone can present it to the service. And it is written in clear text in a log file that all users on the machine can read.
A standard user with access to the Windows machine can therefore retrieve this ticket and use it to execute commands with SYSTEM privileges. Reading the previous sentences, you may have understood that one condition must be met for the flaw to be exploitable: an administrator must have opened the agent in elevated mode and their session must still be active. In practice, the ticket expires when the interface is closed, after an idle timeout, or when the user logs off.
This flaw is useful for taking full control of a machine once a standard account has been compromised, but not for gaining initial access to a machine where the agent is installed.
Which versions are affected, and how can you protect yourself?
Pay close attention to the version numbers, because Veeam mixes those of Veeam Backup & Replication and those of the agent. Bulletin KB4852 states that versions 13.0.1.2067 and earlier in the 13 branch are vulnerable. On the agent side, this corresponds to builds 13.0.2.1102 and earlier, while the fix is included starting with build 13.0.3.1220, according to Veeam Agent for Microsoft Windows security fixes list. That is the version you need to install.
What happens next depends on how the agent is deployed:
- Agent managed by Veeam Backup & Replication: the patch is delivered with Veeam Backup & Replication 13.0.2.29 or later. It’s up to you to check whether the agent update has been applied.
- Standalone agent: the current version is 13.1.1.700, released on August 13, 2026.
Now it’s your turn to patch!