www.it-connect.fr
Popcorn Time Flaw Put Millions of PCs at Risk: CVE-2026-30612 Explained
A forgotten program launched at every startup, capable of executing any file with SYSTEM privileges. That is what Eye Security found on millions of machines running an old version of Popcorn Time. Here’s what you need to know.
Popcorn Time, the BitTorrent-based streaming app that was hugely popular in the mid-2010s, spawned many forks. One of them, Time4Popcorn, was distributed under the Popcorn Time name with closed-source code. It has been abandoned for years... but its update mechanism never stopped running on the machines where it was installed. However, it should not be confused with the new legal project that brought back the Popcorn Time name in early 2025.
It all started during a threat hunting session at a client of Eye Security, a Dutch cybersecurity company. On a laptop, a process Updater.exe was trying to contact popcorntimeupd.xyz, a domain that was no longer registered. The researchers then had an idea: register that domain name. They were able to observe heavy traffic, with about 50 requests per second coming from machines where this process was running.
A real security issue, as we will see later in this article. There is now an assigned CVE reference: CVE-2026-30612. It affects Time4Popcorn up to version 6.2.1.18 on Windows, 6.2.1.17 on macOS, and 3.5.0.173 on Android, with a CVSS score of 9.8 out of 10. And let’s be clear right away: there is no patch, because this project no longer exists.
A HTTP updater with no signature verification
The updater queries its servers over HTTP, retrieves a JSON response pointing to an executable, downloads it, and runs it. Without verifying any signature. Anyone who controls an update domain, or can tamper with the traffic, can therefore push whatever program they want: ransomware, infostealer, or anything else.
- Windows : a service named
Update ServicelaunchesC:\Program Files (x86)\Popcorn Time\Updater.exeorC:\Program Files\Popcorn Time\Updater.exe. The retrieved code runs asNT AUTHORITY\SYSTEM, the highest privilege level on Windows. - macOS : a privileged helper tool,
/Library/PrivilegedHelperTools/PT.updd, runs the code as root. - Android : the updater is built into the app and installation requires user action.
On Windows and macOS, the updater starts with the system: a machine remains exposed even if Popcorn Time has not been opened for years. It is therefore a legitimate channel that can be hijacked to push malicious software.
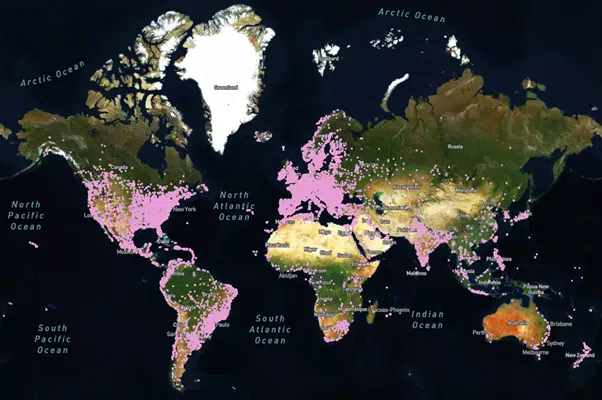
Eye Security believes it identified between 2.5 and 3 million Windows hosts and between 250,000 and 350,000 Macs. "Anyone who registered the right domain could instantly compromise millions of machines".
Operation IXIM: turning the updater against itself
Eye Security’s work did not stop at registering the domain and analyzing how the updater works. First, in June, a report was published explaining how to disable the updater, then Eye Security detailed Operation IXIM at the Hack.lu conference on October 22, 2026. But what exactly does this operation involve?
After consulting its legal department, the Dutch company used the vulnerable mechanism, between November 2025 and March 2026, to deliver code that disables the updater: stopping and disabling the service on Windows, disabling the PT.updd launch daemon on macOS. The security flaw was used against itself to neutralize the process. The point was not to rely on user action, since most users likely would not have done anything.
There was still one small hiccup during the operation: once the code was submitted to VirusTotal, several security solutions blocked it as malicious, leaving the vulnerable updater active. Eye Security had to modify its code to continue the operation.
As of March 1, 2026, received requests had dropped by 98%, with more than 2 million downloads of the update intended to neutralize the updater. By the end of March, Eye Security transferred its 15 domains to the Shadowserver Foundation for sinkholing. Other domains contacted by the updater remain outside its control, however.
In this case, it is important to understand that code was executed on millions of computers without the consent of their owners. Eye Security compares its intervention to Operation Ladybird, during which the Dutch police pushed an update to neutralize the Emotet botnet, while acknowledging one difference: here, users had installed the software voluntarily. “If we did not act, nobody would”, says Niels Teusink.
Finally, if you can: uninstall Time4Popcorn, because even without the updater, Time4Popcorn includes an outdated Chrome engine, makes unencrypted connections, and more. So it is better to remove it completely.
One question remains: was it right to intervene without user consent? What do you think?