www.it-connect.fr
Steam Vulnerabilities Enabled Zero-Click Remote Code Execution on Windows PCs
All it took was two PCs signed into the same Steam account to enable remote code execution on one of them, with no click required from the victim. Researchers at Atredis Partners have disclosed a zero-click flaw in Steam, but that is not all.
On October 28, 2026, Bryan Alexander, a researcher at Atredis Partners, published a technical report titled Turning the Valve, detailing several vulnerabilities discovered in the Steam client on Windows. Part of the work was presented at BSides PDX 2026, and the PoCs were also published on Atredis' GitHub repository.
According to Atredis, Steam has between 35 and 40 million daily active users, making it a globally popular platform. In August, I also published an article about the Metal Gear Online 3 flaw that allowed the host of a Steam lobby to execute code on players' PCs. This time, it is the Steam client itself that is affected by these security issues.
Remote code execution with no click at all
If you use Steam, you know that a Steam account can be signed in on multiple machines at the same time. You simply log in with your credentials on each device. To stay synchronized, clients exchange messages through Valve's Connection Manager infrastructure. It is within this mechanism that the researchers discovered two initial flaws:
- Download scheduling: message 9526 copies a list of application IDs into a fixed-size structure without checking the length. Beyond 200 entries, the return address is overwritten.
- Application status: message 9502 copies progress records into an array of 7 entries. Sending more than that makes it possible to control the RIP register.
These memory corruption issues make it possible to hijack Steam's execution, but the attacker still needs to know where Steam's code is located in memory, something Windows randomizes through a protection called ASLR. A third flaw provides that information. When a Steam client shares its scheduled download list with the other machines on the account, it always sends 32 entries, even if it has fewer. Empty slots are filled with leftover data present in memory, including internal Steam addresses.
The attacker only needs to trigger this send operation to obtain this memory "map," then reuse parts of Steam's code to launch the program of their choice on the other device. The demonstration was carried out from a Windows 10 VM to a fully up-to-date Windows 11 PC.
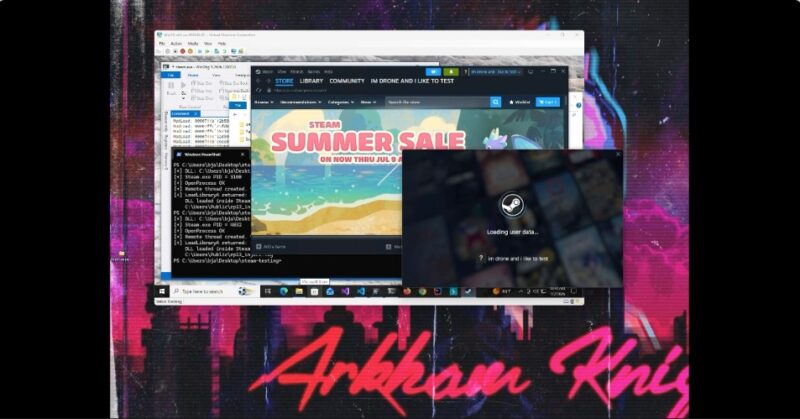
That said, as you probably already guessed, there is an important prerequisite: the attacker must control an authenticated Steam client on the same account as the victim. In other words, the account must first be stolen and signed into, which can be done via an infostealer, since such campaigns are recurring.
Four paths to SYSTEM privileges
The second major part of the report focuses on steamservice.exe, Steam's service that runs as SYSTEM to install game dependencies. Because permissions are too broad, any process can submit requests to it, regardless of integrity level.
- Installation scripts: Steam relies on Valve-signed scripts to install the components games need. The researchers showed that this mechanism could be abused to run a completely different program with SYSTEM privileges. They specifically reused a Valve-signed VDF script (the BioShock Infinite game script in the demonstration).
- Legacy compatibility function: the service launches a program stored in a folder the user can modify, without checking what it is actually executing.
- Secure Desktop: for Remote Play, Steam can forward keyboard and mouse input to Windows' secure desktop, the isolated environment where UAC privilege elevation prompts appear. Once the user allows this option, any program in their session can use it to approve those prompts on its own. "The architecture breaks the isolation boundary imposed by Windows in the secure desktop environment," Bryan Alexander summarizes.
- Steam Frame dongle driver: the function that installs the wireless dongle driver does not verify that it is the correct driver. An attacker can therefore install another signed but vulnerable driver. This is the principle behind a BYOVD attack (Bring Your Own Vulnerable Driver), a technique favored by ransomware groups (example: Akira abusing legitimate Windows drivers to disable Windows Defender).
Note: according to Atredis, two of these privilege escalations were classified as duplicates, and a third had already been reported by another researcher.
Have the vulnerabilities been patched?
Atredis says all the flaws are either fixed or have reached the end of its disclosure window. However, the report does not specify the status of each flaw, the affected versions, or any CVEs. In other words, there is no indication that fixes for these flaws are included in the latest Steam client version...
Ideally, update Steam on Windows, check the list of authorized devices on your account, and most importantly, enable multi-factor authentication.