www.it-connect.fr
PaperCut NG/MF: AI Agents Compromised 395 Organizations Across 48 Countries
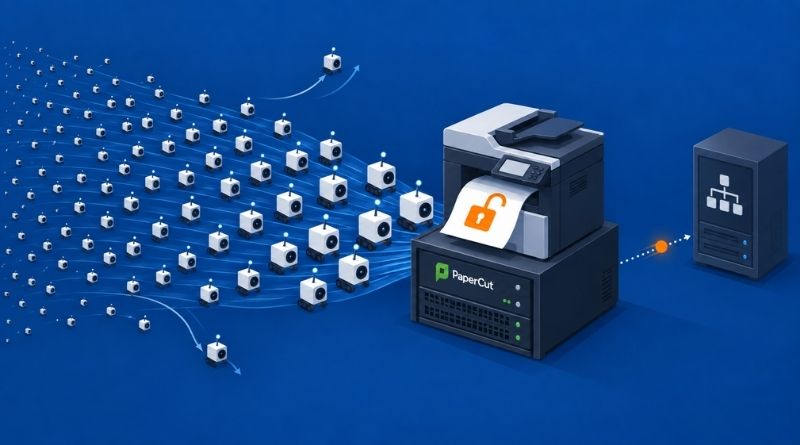
A compromised print server, and 7 minutes later, an Active Directory domain administrator account. A U.S. high school experienced it firsthand. Hundreds of AI agents exploited two flaws in PaperCut NG/MF to compromise at least 440 servers across 395 organizations in 48 countries. France is among them, with 31 victims. Here’s what we know.
If you remember, at the end of August 2026, PaperCut urgently released two patches for its NG and MF products to fix CVE-2026-81578 (authentication bypass) and CVE-2026-82078 (arbitrary Java code execution). I had written about it shortly after, and a report published by Huntress also mentioned early signs of exploitation of these vulnerabilities. What I did not know was that an army of AI agents would automate this vulnerability at scale. That is exactly what happened.
First, let’s ask the obvious question: what makes PaperCut attractive to an attacker? PaperCut NG and MF run by default with SYSTEM privileges on Windows and are most often members of an Active Directory domain. So, in simple terms: compromising the print server means getting a first foothold in the domain.
An attacker and hundreds of AI agents
A new report titled "Agents Gone Wild" published by GreyNoise details an exploitation campaign targeting the two vulnerabilities in PaperCut products. And this time, most of the work was done by AI. It all started with one IP address: 45.142.193.132. GreyNoise has been tracking it since early July 2026, and it is particularly active because it has been associated with attacks against Palo Alto, Ubiquiti, Citrix, SonicWall, and Proxmox VE equipment. Then, on August 31, 2026, it pivoted to a new target: PaperCut.
For large-scale exploitation, the attacker relied on hundreds of AI agents, built on OpenAI’s Codex harness but powered by a DeepSeek model (which is not an OpenAI model; it comes from China). "It is clear that large language models (LLMs) allow malicious actors to move faster and at greater scale.", the report states.
Added to this is an offensive toolkit made up of tools you probably know if you have some knowledge of offensive cybersecurity: Mimikatz, Impacket, Certipy, Rubeus, NetExec, BloodHound, among others. The difference is that everything is orchestrated by AI, and therefore at a speed a human cannot match.
"The attacker went from an empty workspace to the first remote code execution against a real victim in just under four hours, to the first domain administrator account two hours later, and once the full campaign was launched, they compromised at least 11 organizations in 26 seconds", GreyNoise says.
Agents that don’t always obey...
The attacker had given their agents a list of 28 countries not to target, including Russia, China, Hong Kong, Thailand, and Iran, followed by several countries in the Commonwealth of Independent States (which is also what led GreyNoise to suspect a Russian-speaking attacker). But something went wrong: the victim list includes organizations in China, Kazakhstan, Brazil, and Nigeria. In other words, the agents went off the rails.
It is also important to understand that not all attempts led to a truly conclusive outcome. Out of 440 compromised instances, credentials were recovered from 280 organizations, and system or AD domain credentials from 147. Domain administrator status, however, was obtained in only 12 cyberattacks.
To gain domain administrator privileges, three attack paths were used:
- Domain member server: LSASS memory dumping and registry secret extraction to recover privileged credentials, then a pass-the-hash attack against the domain controller.
- Domain not patched against CVE-2021-42278 and CVE-2021-42287. Use of the noPac attack, known since late 2021.
- PaperCut installed on the domain controller itself, or running with a domain admin service account. The attacker simply added their freshly created account to the Domain Admins group.
In all three cases, the next step is the same: a DCSync attack to retrieve the entire NTDS.dit database, 5 to 144 minutes after initial access.
"In at least one case where a vulnerable PaperCut instance was targeted, Cloudflare’s WAF successfully blocked the attacker. Fundamental security hardening of environments remains essential to protect against AI-based threats.", the report says.
Education on the front line, France in third place
After reading all this, you are probably wondering who the targets were. According to GreyNoise’s report, 204 victims belonged to the education sector, including high schools. Geographically, here is what stands out: the United States accounts for 98 affected organizations, followed by the United Kingdom (59), then France and Spain (31 each). In France, the attacker managed to obtain domain administrator privileges in one case.
Finally, note that the ultimate objective remains unknown: resale of access (Initial Access Broker), data theft, or ransomware. By comparison, in 2023, several groups, including Clop and LockBit operators, exploited CVE-2023-27350 on PaperCut servers, with extortion cases in the end.
If you administer a PaperCut NG or MF server, apply the latest available version as soon as possible. Also look for the indicators of compromise published by GreyNoise: the Administrator17 account, pc-*.hiv files in C:\Windows\Temp, or the Ligolo-ng agent in C:\ProgramData. The full list is maintained on GreyNoise’s GitHub repository.