www.it-connect.fr
HBO Max Official Reddit Account Hacked to Push ClickFix Malware Ads
The official HBO Max Reddit account was hacked and used to spread malicious ads for 48 hours. The goal: distribute an infostealer-type malware to Windows and macOS users by exploiting the ClickFix technique. Here’s what we know.
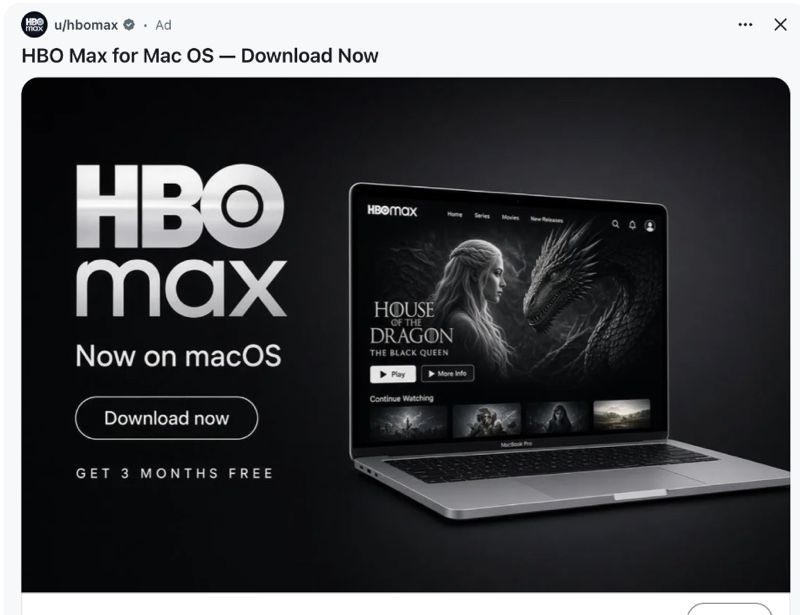
It all started with a Reddit user, Alex Cutts, who noticed an ad that seemed a little too good to be true. That is often the case when an ad is malicious: the offer is meant to be enticing. Yet at first glance, it was reassuring, since the ad was signed u/hbomax, the verified account of Warner Bros Discovery’s streaming platform. The problem is that it promoted a native HBO Max app for macOS, and that app does not exist.
This user shared his discovery on r/cybersecurity: "The ad sends you to hbomaxx[.]us, which looks fairly legitimate, with a button to sign up or download. Clicking it leads to the classic 'paste this command to download' trick used by infostealers and ClickFix.", he wrote. The ad is actually pretty well made (thanks, AI).
As a reminder, ClickFix is a social engineering technique I have already covered several times. The principle, in a nutshell: under the pretext of fixing an error, validating a CAPTCHA, or installing software, the victim copies and pastes a command into the Terminal, PowerShell, or Run box on their PC. In other words, the user infects their own machine.
Here, the hbomaxx[.]us page is a copy of HBO Max’s official website. The download button did not trigger any download, but instead displayed a window asking the user to paste a command into the Terminal.
108 Ads in 48 Hours, and Not Just for HBO Max
A report published by Hudson Rock sheds more light on this malicious campaign. What we learn is that over 48 hours, the u/hbomax account reportedly served 108 separate malicious ads. "The attackers extracted maximum value from the verified status of the account, rapidly switching domains once one was burned.", Hudson Rock summarizes. That number is high, but not surprising: the attackers wanted to move fast and hit hard, especially before HBO Max realized what was happening.
And in reality, the HBO Max app was not the only lure used by the attackers:
- 46 ads pointed to hbomaxx[.]app and hbomax-macos[.]com (streaming).
- 47 ads targeted developers with fake AI tools, via codex-craft[.]com and code-desktop[.]com.
- 15 ads promoted a macOS disk-cleaning utility hosted on apple.clean-disk-guide[.]com.
This official account was therefore used to push ads that had nothing to do with HBO Max. Following reports from users, Reddit took the necessary steps to pause the malicious ads. However, it is still unknown how the attackers gained access to HBO Max’s Reddit account (weak password, infostealer, etc.).
PasteSwitch: A Distribution System That Adapts Malware to the Victim
Hudson Rock’s report also reveals that the HBO Max case is part of a broader campaign called PasteSwitch.
"We can confirm that this incident is part of a large-scale, cross-platform delivery operation that we call PasteSwitch. This operation covers macOS stealers, Windows loaders, misleading TLS tactics, and contract-controlled cryptocurrency clippers.", we read.
The name was not chosen at random, because here is how it works: the victim pastes a command provided by the attacker, and the backend then selects the campaign best suited to that victim. As a result, the payload and monetization method are determined based on the visitor and their system.
On macOS, the command retrieves a script with curl and executes it in zsh. Three payloads were observed by researchers:
- MacSync. An infostealer I covered in December 2025, when an Apple-signed MacSync variant bypassed Gatekeeper. It steals browser credentials, Telegram data, Apple Notes, and macOS passwords.
- AMOS Helper. A native binary that persists in a directory named
.com.apple.accountsdand registers the Mac with a command-and-control (C2) server. - Fake wallet apps. Copies of Ledger, Trezor Suite, and Exodus designed to capture recovery phrases.
On Windows, PasteSwitch uses mshta and PowerShell to load the Amatera infostealer directly into memory, leaving no traces on the PC’s disk. The Amatera malware then contacts its C2 server by IP while presenting facebook.com in the TLS SNI. What is it for? Simply to fool network traffic analysis systems into thinking the connection is headed to Facebook... Clever.
HBO Max has now regained control of its Reddit account, and everything is back to normal.