www.it-connect.fr
Barracuda ESG: Two Chained Flaws Can Lead to Root Access
Do you administer a Barracuda Email Security Gateway appliance, a WAF, or a Load Balancer ADC from this vendor? A security flaw allows commands to be executed as root from an administrator account. But the risk is even greater on ESG, where it can be chained with a second vulnerability that can be exploited without authentication. Here's what you need to know.
On November 2, 2026, Barracuda Networks published a security advisory covering two vulnerabilities in several of its products. The first vulnerability, CVE-2026-116606, is an authentication bypass that affects only the Email Security Gateway (ESG). By exploiting this flaw, a remote unauthenticated attacker can call a configuration import function and restore a forged backup. This allows them to modify the appliance's global configuration.
The second flaw, CVE-2026-111560, is a command injection in the time zone configuration field. It affects six product lines and allows an authenticated administrator to execute commands with root privileges. As you can see, administrative access is already required, which is no small thing.
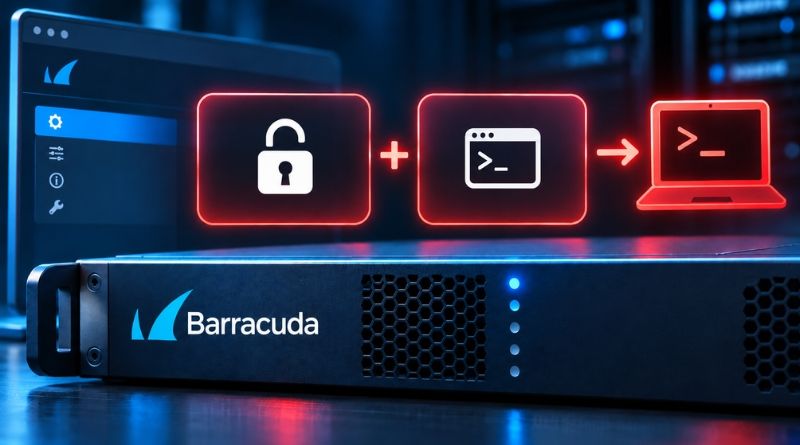
However, there is a greater risk when these flaws are exploited together: "When chained, these vulnerabilities could allow an attacker to bypass authorization controls and gain root access on the device," Barracuda says. The first flaw would provide control over the configuration without prior authentication, while the second would turn administrator access into command execution with root privileges.
Affected Products and Patches to Apply
It should be noted that ESG is the only product affected by both vulnerabilities discussed in this article. The other products listed below are affected only by CVE-2026-111560, which implies that an attacker must already have administrative access (for example, via stolen credentials). Here is a summary:
- Email Security Gateway (ESG) : patch BNSF-40425 for versions 9.4.017 and later, BNSF-40430 for earlier versions.
- Load Balancer ADC : patch BNADC-16586.
- Message Archiver (BMA) : patch BNMA-32468.
- WAF Control Center (WCC) : patch BNWF-60060.
- Web Application Firewall (WAF) : patch BNADC-16586.
- Web Security Gateway (WSG) : patch BNYF-24789.
In terms of severity, the CVE records assign a CVSS 4.0 score of 9.3 to CVE-2026-116606 and a score of 8.6 out of 10 to CVE-2026-111560. To date, no active exploitation has been reported. For its part, CISA considers the first flaw automatable, making it a strong candidate for mass scanning campaigns.
The Administration Interface, the Real Entry Point
The administration interface has always been the entry point. Barracuda also stresses that exploitation requires access to the device's administration interface. Organizations that do not expose it to the Internet are therefore less exposed (as always).
Now you know what you need to do: patch your Barracuda equipment, unless you are using a Cloud version.